Security Testing
Application security audits, penetration testing, vulnerability assessments, OWASP Top 10 compliance, and secure software development lifecycle (SDLC) consulting.
Nexora Labs does NOT promise 100% security, zero vulnerabilities, or unhackable software.
Service Overview & Architecture
Cybersecurity threats evolve constantly, making application security a core engineering discipline rather than an afterthought. Nexora Labs conducts deep Security Testing and Vulnerability Assessments across web applications, mobile platforms, cloud APIs, and enterprise infrastructure. Our security specialists perform manual penetration testing, automated static (SAST) and dynamic (DAST) code analysis, dependency vulnerability scanning, and cloud configuration audits aligned with OWASP Top 10 and NIST guidelines. We identify exploit vectors before malicious actors can discover them and provide practical, prioritized remediation roadmaps.
Production Architecture Blueprint
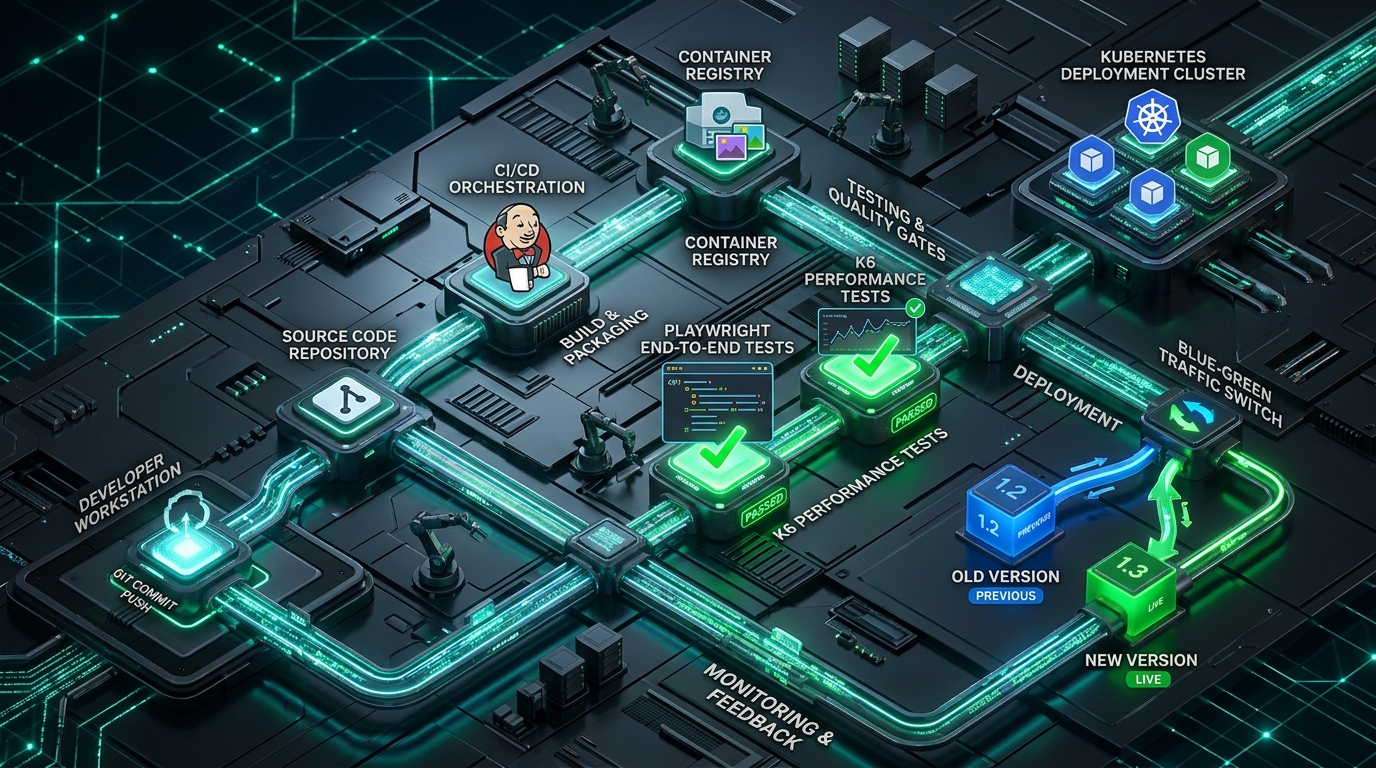
Developer Git Push & PR
GitHub ActionsAutomated linting, SonarQube static analysis, and branch protection rules triggered on every commit.
Challenges We Remediate
- ✕Vulnerability to data breaches, SQL injection, cross-site scripting (XSS), and unauthorized data exfiltration
- ✕Non-compliance with regulatory standards such as HIPAA, GDPR, PCI-DSS, or SOC 2
- ✕Third-party software dependencies containing critical known security vulnerabilities (CVEs)
- ✕Insecure API endpoints exposing sensitive client records without proper authorization checks
- ✕Lack of internal security expertise to conduct pre-launch penetration audits
Core Engineering Capabilities
- Web Application Penetration Testing (OWASP Top 10)
- REST & GraphQL API Security Audits (OWASP API Security Top 10)
- Mobile Application Security Assessment (OWASP MASVS)
- Static & Dynamic Application Security Testing (SAST / DAST)
- Software Composition Analysis (SCA) & Dependency Scanning
- Cloud Security Posture Management & IAM Configuration Audits
- Authentication & Session Management Penetration Testing
Primary Technologies & Frameworks
Concrete Client Deliverables
- •Comprehensive Penetration Testing Report categorized by CVSS severity (Critical, High, Medium, Low)
- •Detailed technical proof-of-concept (PoC) exploit walkthroughs for engineering teams
- •Prioritized remediation recommendations with exact code-level mitigation guidance
- •Executive summary suitable for board presentations and external enterprise client audits
- •Letter of Attestation upon successful remediation and re-testing
How We Deliver: Step-by-Step Methodology
Scoping & Threat Modeling
Defining target assets, boundaries of engagement, attack surfaces, and threat scenarios.
Automated Scanning & Discovery
Executing vulnerability scanners to identify missing patches, open ports, and known CVEs.
Manual Exploitation & Verification
Simulating authentic adversary tactics to test authentication bypass, logic flaws, and privilege escalation.
Risk Assessment & Triage
Rating discovered issues using the Common Vulnerability Scoring System (CVSS v3.1).
Remediation Verification
Conducting re-testing after development teams apply security patches to certify vulnerability resolution.
Commercial Benefits & ROI
Preempt Breaches
Identifies exploitable flaws in private testing before malicious attackers can access customer records.
Regulatory Compliance
Satisfies mandatory annual security penetration testing mandates for SOC 2, HIPAA, and PCI-DSS.
Protected Brand Trust
Demonstrates to enterprise clients that your digital systems undergo rigorous independent security auditing.
Related Case Studies
MediCare Connect: Unified Telehealth & Doctor Appointment Ecosystem
Connecting 85,000+ Patients to Specialized Healthcare Providers with Zero Appointment Delays
FinWise: Next-Generation Digital Banking & Wealth Platform
Modernizing Retail Banking for 420,000 Account Holders with Zero-Trust Security
RetailPulse: Omnichannel Inventory & Headless Commerce Platform
Harmonizing 140 Physical Stores with Sub-Second Real-Time Headless Commerce
Frequently Asked Questions About Security Testing
Ready to Leverage Our Security Testing Practice?
Schedule a 30-minute discovery call to scope your technical backlog and timeline.